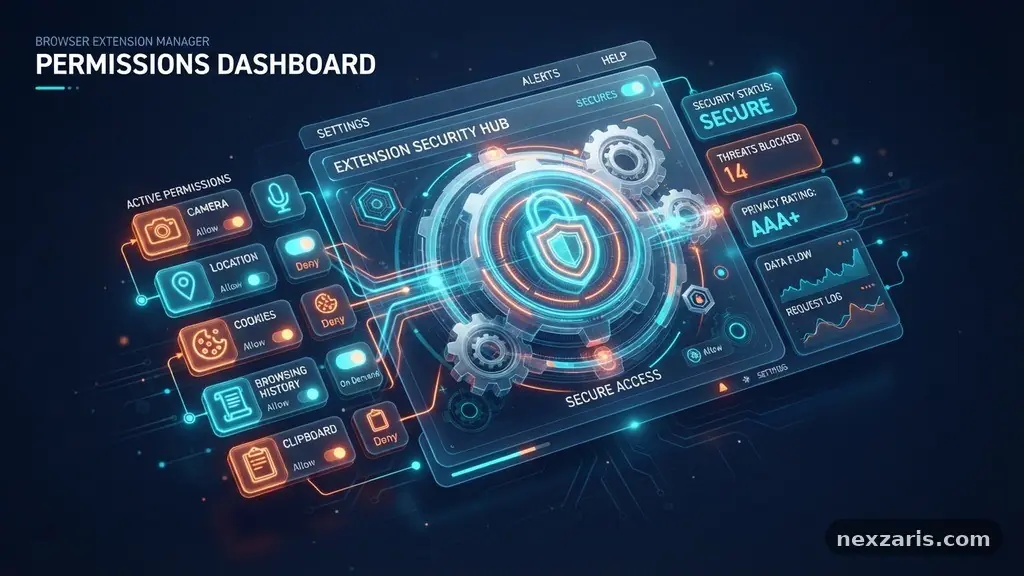
How to Keep Browser Extensions From Becoming a Security Risk
Managing your digital footprint requires careful attention to browser extensions, which often act as silent gateways to your personal information. By understanding how to keep Browser Extensions From Becoming a Security Risk, you can significantly reduce the surface area for potential attacks while maintaining the productivity features you rely on daily.
This article provides actionable steps to audit your current setup and implement stricter controls, ensuring your browsing experience remains both functional and secure. You will learn how to identify suspicious add-ons and restrict the data they can access, ultimately protecting your passwords and private browsing history from unauthorized exposure.
The Mechanics of Extension Permissions
When you install an add-on, you are essentially granting a third-party developer a window into your digital life. These tools often request broad capabilities, such as the ability to read and change website data, which allows them to function correctly on the pages you visit.
However, this same power can be exploited if the extension is malicious or has been compromised by a bad actor. Understanding these permissions is the first step in effective browser hardening, as it forces you to acknowledge that every tool you add creates a new potential vulnerability.
Many users instinctively click “Add to Chrome” without reading the requested permissions prompt. This dialogue box often hides critical details, such as whether an extension can view your passwords or track your browsing activity across all websites.
By taking a moment to review these requests, you can decide whether the functionality justifies the level of access being granted. If an extension asks for access that seems unrelated to its primary purpose, such as a simple calculator app asking for permission to read your history, it is best to avoid it entirely.

Strategies for Minimizing Browser Risks
Adopting a disciplined approach to your browser environment is essential for maintaining long-term security. One of the most effective Strategies for Minimizing Browser Risks is to limit the total number of extensions you keep active at any given time.
Every extra piece of software is a potential entry point for hackers, especially if the developer stops updating the code. It is far safer to use a few well-vetted, highly-rated tools than to clutter your browser with dozens of obscure plugins that you rarely use.
You should also look for extensions that are open-source or maintained by reputable organizations with a track record of transparency. When an extension is open-source, the community can inspect the code for vulnerabilities, making it harder for malicious actors to hide backdoors.
Additionally, check the update frequency of any tool you consider installing. If an extension hasn’t received an update in more than a year, it is likely abandoned and should be removed from your system to prevent it from becoming a target.
Audit Your Existing Extensions
Regular maintenance is just as important as initial vetting when it comes to your browser’s security. You should set aside time once every few months to Audit Your Existing Extensions and clear out anything that no longer serves a clear, necessary purpose.
During this process, be ruthless about deleting tools that you cannot remember installing or those that have become redundant over time. If you do not recognize an extension or cannot recall the last time you used it, remove it immediately.
This audit should also involve checking the permissions of the extensions you choose to keep. You can often modify these permissions in the browser settings to restrict access to specific sites rather than allowing the extension to run on every page you visit.
For instance, if you have a price-tracking tool, configure it to only run on specific shopping websites. By limiting the scope of these tools, you ensure that even if one of them is compromised, the impact on your overall privacy remains minimal.
Identifying Signs of Malicious Activity
Recognizing when an extension has turned rogue is a critical skill for any security-conscious user. Identifying Signs of Malicious Activity often involves noticing subtle changes in your browsing experience, such as unexplained pop-ups or search engine redirects.
If your browser suddenly starts injecting ads into websites where they do not belong, it is a strong indicator that one of your installed extensions has been hijacked. You should also watch for unexpected changes in your browser’s homepage or the appearance of toolbars that you did not explicitly authorize.
Another warning sign is a sudden surge in system resource usage. If your computer slows down significantly whenever you open a new tab, a background extension might be running unauthorized processes, such as cryptomining or data harvesting.
In these cases, check your task manager or browser-specific process viewer to see which extensions are consuming the most memory or CPU. If you find something suspicious, do not hesitate to disable it and run a full security scan of your device to ensure no secondary malware was installed.
Implementing Least Privilege Access
The principle of least privilege is a cornerstone of cybersecurity, and it applies perfectly to your browser configuration. Implementing Least Privilege Access means giving every extension only the bare minimum permissions required to perform its job.
For example, a password manager clearly needs access to your credentials, but it should not need the ability to read your history or track your clicks on external websites. By manually restricting these permissions, you create a layer of defense that keeps your sensitive data isolated.
Modern browsers have made it easier to manage these constraints through their settings menus. You can often toggle “On click” permissions, which prevents an extension from running automatically until you manually activate it for a specific session.
This is an excellent way to maintain convenience without sacrificing your overall security posture. By being intentional about when these tools are active, you regain control over the information that is shared with third-party developers, ensuring your browser remains a secure environment.
The Role of Official Repositories
The Chrome Web Store and similar official repositories serve as the primary gatekeepers for browser safety, but they are not infallible. While these platforms do perform automated scans to catch common threats, malicious add-ons can occasionally slip through the cracks.
It is important to treat even store-verified extensions with a healthy dose of skepticism. Always check the user reviews, the number of active users, and the developer’s reputation before hitting the install button.
If an extension has very few reviews or a suspicious lack of developer information, it should be treated as a potential risk. Furthermore, be wary of “copycat” extensions that mimic the names and logos of popular, trusted tools.
These are often designed to trick users into installing software that steals data or redirects traffic. Always double-check the developer’s name and the official website associated with the extension to ensure you are installing the legitimate version of the software rather than a fraudulent clone.
Data Privacy and Browser Hardening
Protecting your data privacy requires a holistic approach to browser hardening that goes beyond just managing extensions. While managing your plugins is a vital part of the process, you must also be mindful of how your browser itself handles cookies, cache, and site permissions.
Many extensions rely on these underlying data sources to function, so keeping your browser updated to the latest version is essential. Updates often contain security patches that prevent extensions from exploiting known vulnerabilities in the browser’s code.
The following table provides a quick reference for common extension risks and how to mitigate them effectively.
| Risk Category | Potential Impact | Mitigation Strategy |
|---|---|---|
| Over-permissioned tools | Data leakage / Tracking | Set permissions to “On Click” only. |
| Abandoned extensions | Exploitable vulnerabilities | Remove any tool unused for 30+ days. |
| Malicious clones | Credential theft | Verify developer and official site. |
| Adware injection | Browser hijacking | Audit and remove suspicious plugins. |
By maintaining a clean browser environment, you ensure that your personal information remains under your control. Remember these key practices to stay secure:
- Review requested permissions before clicking install.
- Disable or remove extensions you no longer use daily.
- Use only extensions from well-known, verified developers.
- Check your browser settings for “site access” restrictions.
- Regularly update your browser to the latest secure version.
Frequently Asked Questions
How can I tell if an extension is spying on me?
Watch for unusual behavior such as unexpected redirects, new toolbars appearing, or your browser suddenly becoming sluggish. If you notice these symptoms, open your extensions manager and disable them one by one to isolate the culprit. If an extension is sending data to unauthorized servers, you might also see increased network activity in your system’s resource monitor.
Is it safe to use extensions from the official store?
While official stores are generally safe, they are not perfect. Malicious developers sometimes bypass security checks, so you should still exercise caution. Always research the developer’s background, read recent user reviews, and check how long the extension has been available before deciding to install it.
What should I do if I suspect an extension is malicious?
If you suspect an extension is compromised, remove it immediately from your browser settings. After removal, clear your browser’s cache and cookies to ensure no residual data is being tracked. If you are concerned that your passwords or financial information were accessed, change those credentials immediately from a different, secure device.
Do I need to worry about extensions I don’t use often?
Yes, even inactive extensions can pose a risk if they remain installed. If an extension is not being actively updated by its developer, it could contain vulnerabilities that hackers can exploit. It is best practice to keep your extension list lean and remove anything you are not actively using to minimize your security footprint.
Can I limit what websites an extension can access?
Yes, most modern browsers allow you to restrict an extension’s access to specific websites or require your permission before it runs. You can usually find these settings by right-clicking the extension icon or navigating to your browser’s “Manage Extensions” menu. Limiting access ensures that the extension only interacts with the sites where it is actually needed.
Maintaining Your Digital Security
Taking control of your browser environment is one of the most effective ways to protect your personal information online. By consistently applying the strategies for keeping Browser Extensions From Becoming a Security Risk, you ensure that your productivity tools remain assets rather than liabilities. Remember that security is not a one-time setup but an ongoing habit of auditing your tools and staying informed about potential threats.
Start today by reviewing your currently installed extensions and removing anything that feels unnecessary or suspicious. By limiting permissions and sticking to reputable sources, you build a much stronger defense against data breaches and unauthorized tracking.
If you have questions about specific tools or notice something strange in your browser, do not hesitate to reach out to official support channels or community forums for guidance. Keeping your digital life secure is well worth the effort.